
 Reeve
Security basics
ERR_TOO_MANY_REDIRECTS on a custom domain behind Cloudflare
ERR_TOO_MANY_REDIRECTS after you put Cloudflare in front of your site: why the loop happens, and the fix that keeps your sign-ins encrypted.
In short
- ERR_TOO_MANY_REDIRECTS means Chrome was sent from address to address 20 times for one page and gave up. Behind Cloudflare, a common cause is its Flexible setting meeting a host that sends plain HTTP on to HTTPS.
- Chrome suggests deleting your cookies. That ends a loop one browser carries, and a loop in your Cloudflare settings reaches every visitor whatever their cookies hold.
- Cloudflare offers two fixes for a Flexible loop. Removing your host's HTTPS redirect makes the page load and leaves the leg from Cloudflare to your host unencrypted. Use Full (strict), or set the record to DNS only.
You put your domain behind Cloudflare, or changed one setting there, and now
your app opens on a grey page. "This page isn't working", it says, then
"yourapp.com redirected you too many times.", and at the bottom a code:
ERR_TOO_MANY_REDIRECTS. Chrome offers one suggestion: "Try deleting your
cookies." You delete them, reload, and the page is still there, for you and for
the customer who sent you the screenshot.
Cloudflare's own troubleshooting page gives two fixes for the loop its Flexible setting causes, and both bring the page back. One of them also leaves every password your visitors type travelling part of the way unencrypted. It is the quicker one, which is why it is worth knowing before you reach for it.
Picture Cloudflare as a reception desk in front of your office. Visitors come in through the front door, which is HTTPS: the padlock in the address bar, a connection nobody along the way can read. Reception then takes each request on to your office, which is your host (Lovable, Vercel, Netlify, wherever the app actually runs). How reception gets there is a Cloudflare setting, and the visitor never sees that part of the trip.
What does ERR_TOO_MANY_REDIRECTS mean?
It means the browser was sent from one address to another so many times that it stopped trying. Chrome stops at 20.
A redirect is an answer that says "not here, go to this address instead",
and the browser follows it without asking you. Chrome's source caps the chain at
20 for one page and quotes the web's Fetch standard beside the number: "If
request's redirect count is twenty, return a network error." What you see then
is "This page isn't working", your site's name with "redirected you too many
times.", and ERR_TOO_MANY_REDIRECTS at the bottom. Cloudflare's page on the
error gives a second wording you may meet, "The page isn't redirecting
properly".
The heading is worth reading. When Chrome gets nothing back from your address, it says "This site can't be reached" instead. Here the browser did reach your site, twenty times over, and every answer sent it on somewhere else. In the building, the visitor was walked between two doors until the browser gave up counting.
Will deleting your cookies fix it?
Only if the loop lives in one browser. A loop in your settings reaches every visitor, and their cookies play no part in it.
A cookie is a small note your app leaves in a visitor's browser, such as the one that keeps somebody signed in. Chrome's page for this error adds "Try deleting your cookies", and Firefox's says "This problem can sometimes be caused by disabling or refusing to accept cookies." Both are written for the person looking at the error. When the site is yours, the first question is whether everybody sees it.
Test it where your own cookies cannot reach:
- Open your site in a private window. It starts with none of your normal window's cookies.
- Open it on your phone over mobile data, off your home Wi-Fi.
- If both loop, the cause is in your settings, and the rest of this post is about where.
Why does Cloudflare's Flexible mode cause a redirect loop?
Because Flexible makes Cloudflare fetch your pages from your host over plain HTTP, and a host that insists on HTTPS answers plain HTTP with a redirect to HTTPS.
When a record in Cloudflare's DNS has the orange cloud switched on (Proxied), visitors connect to Cloudflare, and Cloudflare makes a second connection to your host. Cloudflare's SSL/TLS encryption mode decides how that second connection is made. In Cloudflare's words, Flexible means "Cloudflare allows HTTPS connections between your visitor and Cloudflare, but all connections between Cloudflare and your origin are made through HTTP." The origin is your host.
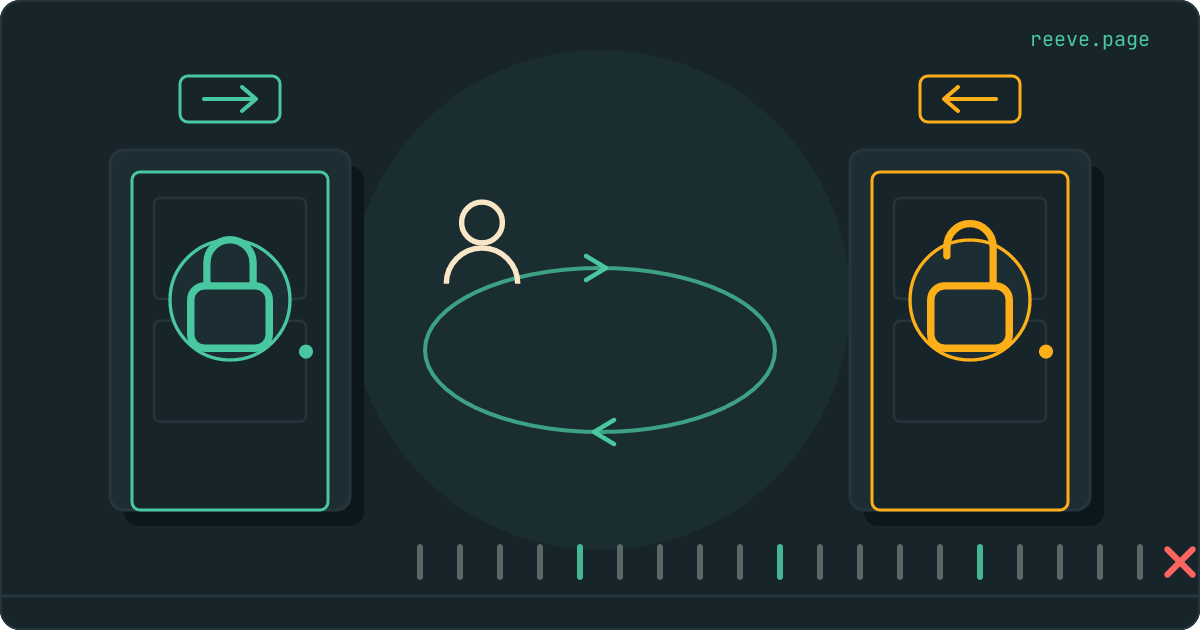
Back in the building, reception carries every request up the back stairs, which is plain HTTP. Your office has one rule: anyone arriving on the back stairs is sent round to the front door. The visitor already came in that way, so reception takes them up the back stairs again. Vercel's guide to running Cloudflare in front of it describes exactly this: "Flexible mode can cause a redirect loop: Cloudflare connects to Vercel over HTTP, Vercel redirects to HTTPS, and the cycle repeats."
Cloudflare's page on Flexible puts it in a caution box: "If your origin forces HTTPS by automatically redirecting HTTP requests to HTTPS, do not use Flexible mode." Doing so, it adds, "creates a redirect loop that makes your site inaccessible."
Which other Cloudflare settings loop?
Four more, all from the same page of Cloudflare's documentation. In every row, two parties send the visitor opposite ways.
| Setting in Cloudflare | It loops when | Cloudflare's fix |
|---|---|---|
| Full or Full (strict) encryption mode | your host sends HTTPS requests to HTTP | Remove that redirect at your host |
Always Use HTTPS, which sends every http request to https | your host sends HTTPS requests to HTTP | Remove that redirect, or turn Always Use HTTPS off |
| HSTS, a header telling browsers to use HTTPS only | your host sends HTTPS requests to HTTP, or the encryption mode is Off | Remove the redirect and choose any mode above Off, or turn HSTS off |
| Redirect rules and Page Rules | two rules send visitors to each other | Review the rules until none of them conflict |
The last row is the one your builder's own settings can join. Lovable sends
every domain connected to a project on to the one you marked primary. Suppose
yourapp.com is primary and a Cloudflare rule sends yourapp.com to
www.yourapp.com. Lovable sends the visitor back, the rule sends them forward,
and the browser counts to 20.
Which fix keeps your visitors' sign-ins encrypted?
Full (strict), or taking Cloudflare out of the path with DNS only. Cloudflare's other fix for a Flexible loop makes the page load and leaves the second leg in plain HTTP.
The troubleshooting page lists both: "either remove HTTPS redirects from your origin server or update your SSL/TLS Encryption Mode to be Full or higher". The first looks quicker, since nothing at Cloudflare changes. In the building, it takes the rule off your office door so the back stairs work, and everything said on the stairs can be overheard: the email and password in a sign-in form, and the page that comes back with somebody's account on it. Cloudflare's description of Flexible says it "makes your site partially secure", and adds: "If your application contains sensitive information (personalized data, user login), use Full or Full (Strict) modes instead."
Your visitors cannot tell: the padlock in their address bar is about the front door only.
Full encrypts the second leg without checking who answers at the other end. Cloudflare's page on it says "The certificate presented by the origin will not be validated in any way", and warns that "Without using Full (strict), a malicious party could technically hijack the connection and present their own certificate." A certificate is the ID your host shows to prove which site it is. Full (strict) checks that ID: unexpired, issued by a publicly trusted authority or by Cloudflare's own Origin CA, and naming your domain. Cloudflare's advice is to "choose Full (strict) mode whenever possible".
| What you set | Between Cloudflare and your host |
|---|---|
| Flexible, with your host's HTTPS redirect removed | Plain HTTP |
| Full | Encrypted, and your host's certificate is not checked |
| Full (strict) | Encrypted, and your host's certificate is checked |
| DNS only (grey cloud) | No second leg: visitors connect straight to your host over its own HTTPS |
How do you fix ERR_TOO_MANY_REDIRECTS on Lovable or Vercel?
Set the records to DNS only, which both Lovable and Vercel describe, or keep the proxy and set the encryption mode to Full (strict).
- See which setup you have. In Cloudflare, open your domain's DNS records. The proxy status beside each record is an orange cloud (Proxied) or a grey one (DNS only). Then open the SSL/TLS Overview page for the encryption mode.
- To take Cloudflare out of the path, switch the records your host gave you to DNS only. Vercel's guide says you "can keep Cloudflare as your DNS provider without enabling its reverse proxy", and asks you first to confirm that Vercel "presents a publicly trusted certificate for the hostname". Lovable installs a certificate for every custom domain it connects, and its answer to Cloudflare errors on a Lovable domain is this same switch, to "DNS only (gray cloud) instead of Proxied (orange cloud)".
- To keep Cloudflare in front, choose Full (strict) on that Overview page. Depending on your account, the page may offer Automatic SSL/TLS, which picks a mode by testing your host, beside Custom SSL/TLS, where you pick it. Vercel's guide asks for Full (strict). On Lovable, the proxy route is the Uses Cloudflare or similar proxy option when you connect the domain, and Lovable's documentation says "Lovable does not configure, validate, or monitor your CDN or proxy setup", so the mode is yours to set. If your host has no valid certificate for the name, visitors may get Cloudflare's error 526 instead of your page.
- Look for a rule pointing the other way. In Cloudflare's redirect rules
and Page Rules, find anything that moves visitors between
wwwand the bare domain against your host's own setting. - Test again in a private window and on mobile data.
Once your site loads again, our free scan reads it from outside, the way a visitor's browser does, and reports your certificate's end date and whether your site sends HSTS. It takes about 20 seconds and needs no account: scan your app.
Keeping an eye on it after the fix
Cloudflare settings change without a deploy, so the check worth repeating is what your site sends from outside.
The free scan reads your live site the way a visitor's browser does.
- It reports your certificate's end date and the security headers your site sends, HSTS among them.
- There is no account to make and nothing to install.
Scan your app free in 20 seconds
Reeve Monitor runs that security check every hour and tells you when your grade drops.
- The alert names your grade before and after.
- It warns you before your SSL certificate lapses.
- Alerts go out by email, Telegram, Slack or webhook.
What to do right now
What to do
- Read the heading before you change anything. "This page isn't working" with
ERR_TOO_MANY_REDIRECTSmeans your site answered, and kept sending the browser somewhere else. - Open the site in a private window and on mobile data. If it loops there as well, deleting cookies will not fix it.
- In Cloudflare, check the proxy status of your records and the SSL/TLS encryption mode.
- Set the records to DNS only, or keep the proxy and choose Full (strict).
- Leave your host's HTTPS redirect in place. Removing it ends a Flexible loop by sending your visitors' sign-ins over plain HTTP.
- Look for a Cloudflare redirect rule that disagrees with your host's own redirect between
wwwand the bare domain.
If the browser now warns about a certificate instead, read the three causes besides expiry: a proxy in front of your host is one of them.
FAQ
What does ERR_TOO_MANY_REDIRECTS mean?
Your site kept answering with "go to this other address instead", and Chrome stopped following after 20 of those answers for one page. The heading on the page is "This page isn't working", with your site's name and "redirected you too many times." under it. It means your site was reached and every answer sent the browser somewhere else.
Will clearing my cookies fix "redirected you too many times"?
Only when the loop lives in one browser, which is the case Chrome's suggestion is written for. Open your site in a private window and on mobile data. If it loops there too, the cause is in your settings, at Cloudflare or in a redirect rule, and deleting cookies changes nothing.
Why did my site start looping when I turned on Cloudflare?
With the orange cloud on, Cloudflare connects to your host for every visitor. In Flexible mode it makes that connection over plain HTTP, and a host that only serves HTTPS answers with a redirect to HTTPS. The visitor already came in over HTTPS, Cloudflare asks over HTTP again, and the two keep sending the browser round.
Is Cloudflare's Flexible SSL mode safe?
It encrypts the connection between your visitor and Cloudflare only. Cloudflare's own documentation says Flexible "makes your site partially secure" and tells sites with personal data or user logins to use Full or Full (strict) instead. Of those two, only Full (strict) checks the certificate your host presents.
Should I use DNS only or Full (strict) for a Lovable or Vercel app?
Either works. DNS only takes Cloudflare out of the path, and both Lovable and Vercel describe it; Vercel asks you to confirm it shows a trusted certificate for the domain before you switch. Full (strict) keeps Cloudflare in front and needs your host to present a valid certificate for the name, which Vercel's guide asks for.