
 Reeve
Security, in plain language
Short write-ups about what actually goes wrong in AI-built apps, and what to do about it.
Page 2 of 5
Why you can't download your Supabase backup
You can't download your Supabase backup on a current project, because the daily copy is a physical snapshot. How to tell, and how to hold a copy of your own.
Supabase "permission denied for table": the missing grant
From October 30, a new Supabase table answers "permission denied for table" until you grant access. The grant the email shows is half the fix.
Is an open API endpoint a security problem? Look at the JSON
Your scan flagged an open API endpoint. Whether it matters depends on what came back, and most of the ones we found were the platform's own.
Lovable security scan: the one thing it cannot prove
Lovable security scan: what the Quick and Deep scans check, when each one runs, and the one thing no scan from inside your project can prove.
Why your Supabase dump has no users in it
Run supabase db dump on its own and you get the shape of your database and none of its rows, with the auth schema your users live in left out entirely.
Domain expired, website down: what actually happens next
Your domain expired and your website is down. Here is the clock you are on, why a lapsed certificate is the easier of the two, and how to check both.
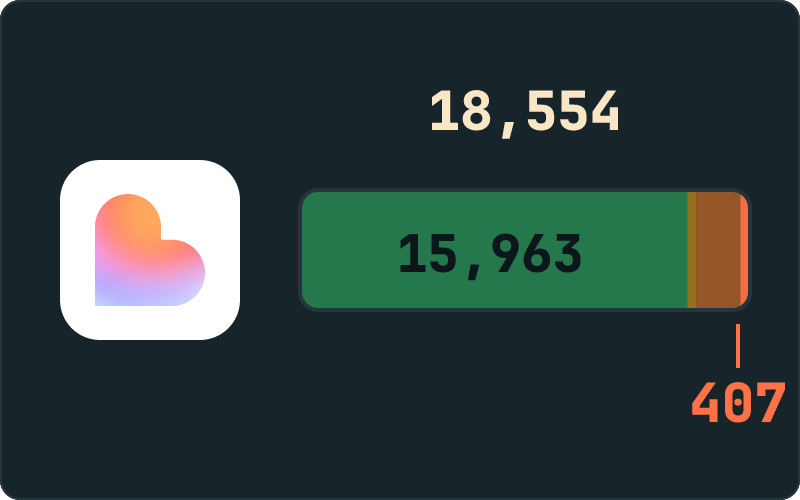
Is Lovable safe? What 18,554 live Lovable apps showed
Is Lovable safe? We ran nine checks on 18,554 live Lovable apps. The platform was the cleanest of five builders. Every finding was inside the app itself.
The vibe coding security checklist, in nine checks
A vibe coding security checklist with nine items, each one something anyone can verify about your live app from outside, and each with a one-line test.
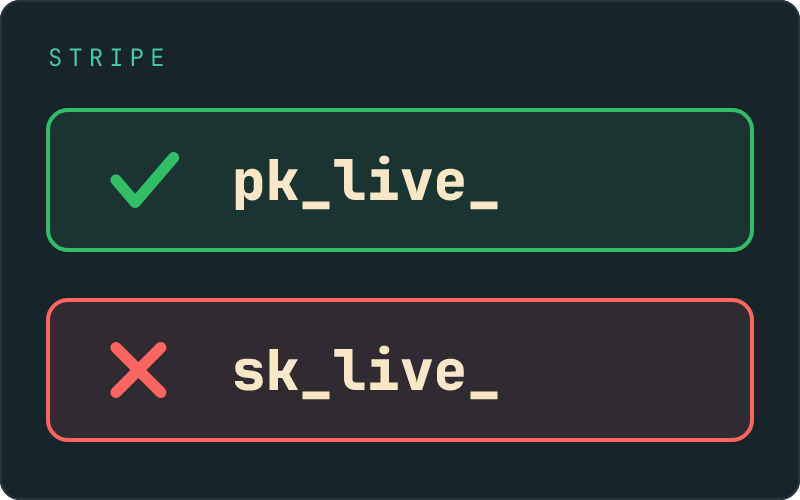
A Stripe secret key exposed in your frontend can move money
A Stripe secret key exposed in your frontend can refund, charge and read every customer record you hold. Your pk_live_ key is meant to be there.
Vite env variables exposed: VITE_ and NEXT_PUBLIC_ mean publish this
Vite env variables exposed in your app did what the prefix asked. VITE_ and NEXT_PUBLIC_ mean publish this, and the AI that added one never knew the cost.
Base44 security: what a scan flags, and what is yours to fix
Base44 security on 5,438 scanned apps: three findings on nearly every one are the platform's, the source map is Base44's badge, and what is yours is short.
Is Cursor AI safe? The editor, the code, and the app you shipped
Is Cursor AI safe? Three questions in one search: what Cursor keeps, what the code it writes gets wrong, and whether the app you shipped is open.
Is Replit safe? What we found in 3,042 live Replit apps
Is Replit safe? We ran nine external checks on 3,042 live Replit apps. The host was not where the findings were. The app each owner published was.
Supabase storage backup: why your database copy has no files
A Supabase storage backup is a separate job. Database backups keep the list of your files and none of the files, so a restore leaves every upload broken.
Supabase point-in-time recovery: what it costs, what it misses
Supabase point-in-time recovery rewinds your database to any second in the last week. It costs $100 a month on top of Pro, and it covers your database only.
Everything here is written by a security expert, and aimed at whoever pressed deploy.
Vlad Tkachenko