
 Reeve
Security, in plain language
Short write-ups about what actually goes wrong in AI-built apps, and what to do about it.
Page 6 of 7
Supabase "RLS disabled in public": what the warning misses
Supabase reports "RLS disabled in public" as an error. It says nothing about the read policy that leaves your table just as open to strangers.
How to rotate a leaked Supabase service_role key
Supabase says fix the leak first. Other guides say rotate now. Which is right depends on where your service_role key leaked.
Vibe coding security scanners compared, including ours
The best vibe coding security scanner comes down to three questions no feature list answers. Eight tools compared, with prices, and the jobs Reeve does not do.
Supabase security checker: run the five checks yourself
A Supabase security checker reads your published app instead of your project settings. Here are the five checks it runs, and how to run each one yourself.
Vibe coding security scanner: what a URL scan misses
A vibe coding security scanner reads your live app from outside. Here is what that covers, the four things it cannot see, and how to read the result.
Missing security headers: when it actually matters
Missing security headers is the finding our scanner prints most. Here is what it protects against, and when it is the least urgent line on your report.
Your OpenAI API key is exposed in your frontend. Rotate it.
An OpenAI API key exposed in your frontend cannot be locked to a domain. Rotate it today, move the call behind your own endpoint, and cap the spend.
An API key exposed in your frontend: what 30,998 apps shipped
An API key exposed in your frontend is usually a Google Maps key. We scanned 30,998 live vibe-coded apps and counted which secrets actually leak.
Supabase backup tools compared, including ours
Four kinds of Supabase backup tool, what each one actually copies, and the case where a free GitHub Action beats paying anyone, us included.
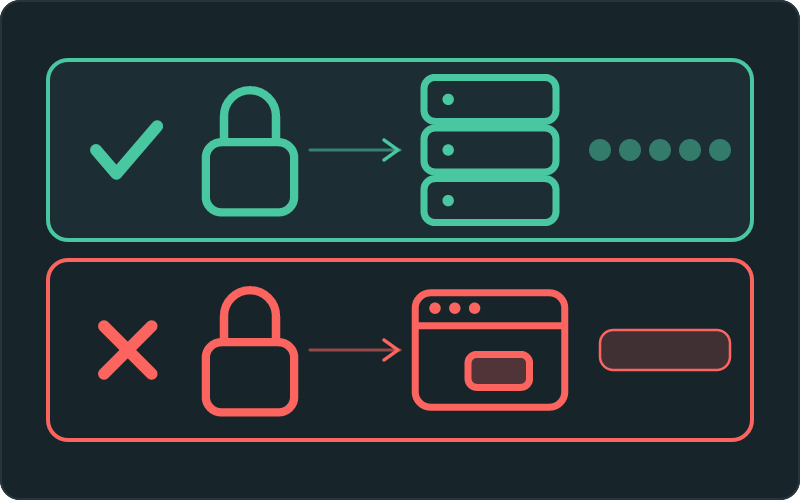
How to use secrets in Replit, and what still gets published
How to use secrets in Replit: add one, read it back, and fix the two reasons it comes back undefined. Plus the keys the Secrets tool cannot keep private.
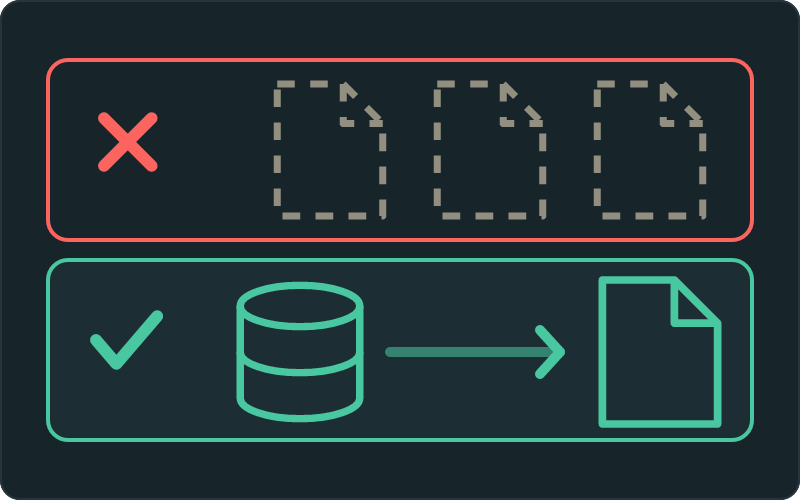
Supabase free tier backups: how to make one without a terminal
There are no Supabase free tier backups, so the copy has to come from you. How to make one from the dashboard, and what CSV leaves out.
Is Supabase secure? Yes. Your project is a separate question
Is Supabase secure? The platform is audited, encrypted and pen-tested. Their own compliance documents say where that stops and your settings begin.
Where to find your Supabase URL, publishable and secret keys
Your Supabase project URL, anon key and service_role key are on one dashboard page. Here is where that page is, and which of the four belongs in your app.
New row violates row-level security policy in Supabase. Now what?
"New row violates row-level security policy" means Supabase refused a write. The fix that clears it in ten seconds also reopens the table to everyone.
Is a CORS wildcard a security risk? Usually not.
Is a CORS wildcard a security risk? Usually it is your builder default, and it gives away nothing your server was not already handing to anyone who asked.
Everything here is written by a security expert, and aimed at whoever pressed deploy.
Vlad Tkachenko